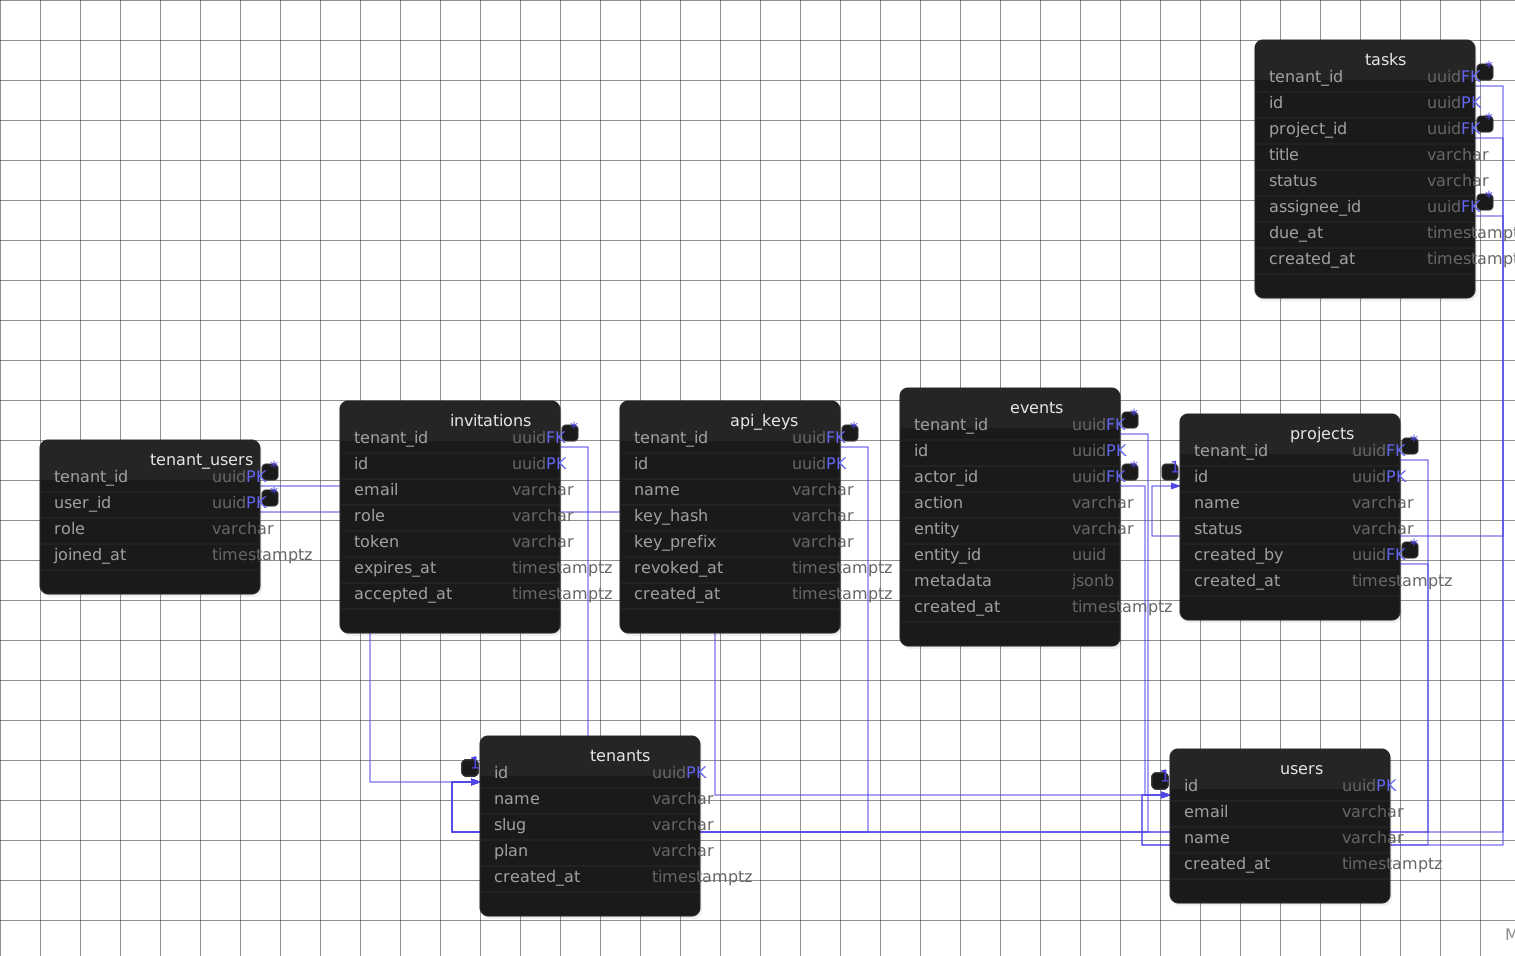
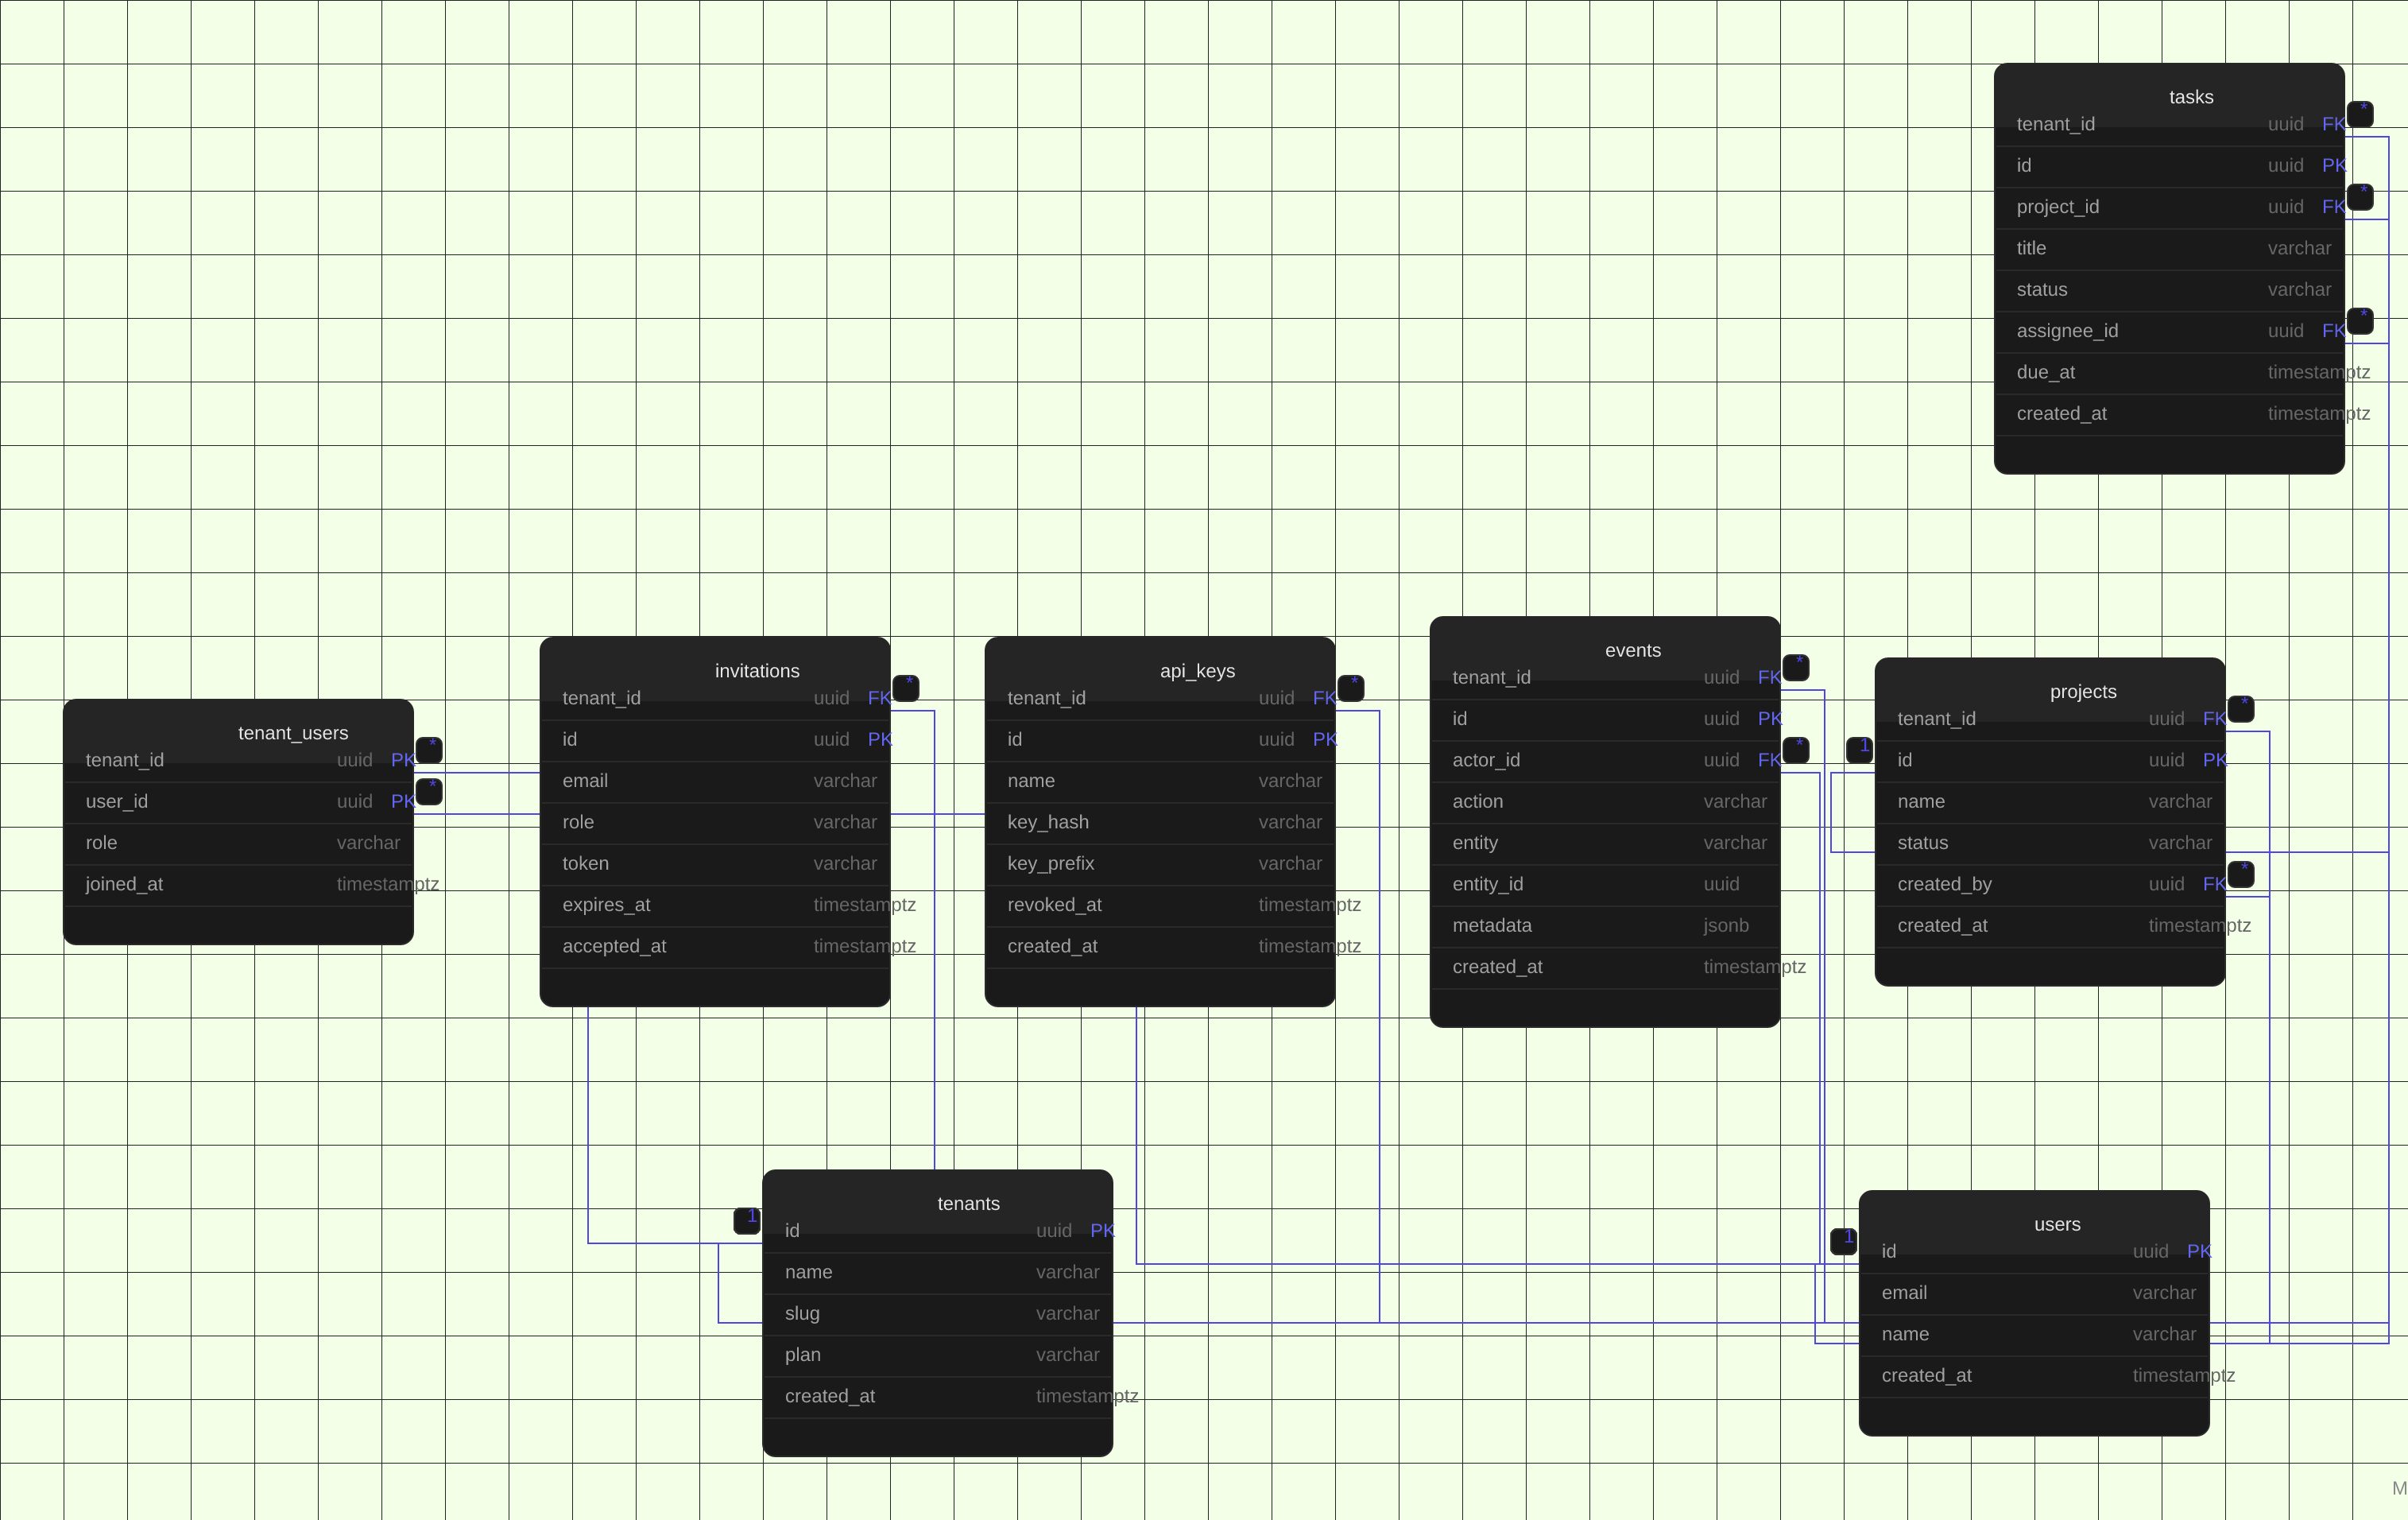
The DDL on this page is the simpler starting point. To stop one tenant's rows from referencing another tenant's rows, add a composite unique key to the parent and a composite foreign key on the child. This example hardens tasks.project_id:
alter table projects
  add constraint projects_tenant_id_id_key unique (tenant_id, id);

alter table tasks
  drop constraint fk_tasks_project_id;

alter table tasks
  add constraint tasks_tenant_project_fk
  foreign key (tenant_id, project_id)
  references projects (tenant_id, id);
The composite key makes the tenant part of the reference. A task can now point only at a project in its own tenant. Apply the same pattern to every tenant-owned foreign key.
Row-level security adds a second layer. Store the current tenant in a session setting, then filter every row through it:
alter table tasks enable row level security;

create policy tasks_tenant_isolation on tasks
  using (tenant_id = current_setting('app.tenant_id', true)::uuid)
  with check (tenant_id = current_setting('app.tenant_id', true)::uuid);
Set app.tenant_id on each request before querying, for example select set_config('app.tenant_id', $1, true);. If the setting is missing, current_setting(..., true) returns null and the policy matches no rows.